Security Operations01
SOC Monitoring Workflow
A structured SOC-style monitoring concept covering alert review, triage, investigation and escalation using SIEM-oriented thinking.
WazuhSIEMThreat Analysis
VIEW PROJECT DETAILS
Cybersecurity Analyst | Project Manager
I work at the intersection of security, execution and communication — translating technical risk into structured action, coordinating delivery, and building security-aware workflows that teams can actually use.
Security, delivery and technical fluency — organized around outcomes rather than labels.
Coordinating project delivery while supporting cybersecurity analysis, security monitoring, incident-oriented workflows and technical communication across teams.
Worked across multidisciplinary production teams, coordinating schedules, deliverables, approvals and quality while supporting complex technical pipelines and client-facing execution.
Taught technical and creative workflows, translating complex processes into structured learning material and practical production guidance.
A curated set of security and delivery-oriented portfolio case studies reflecting the way I approach technical work.
A structured SOC-style monitoring concept covering alert review, triage, investigation and escalation using SIEM-oriented thinking.
A repeatable review workflow for common web application risks, findings prioritization and remediation communication.
A defensible digital evidence process centered on identification, preservation, analysis, reconstruction and reporting.
A practical delivery structure for scope, milestones, stakeholder updates, risks, approvals and handoff quality.
A portfolio lab concept focused on traffic visibility, anomaly review and security-tool correlation across network events.
A security assessment framework for discovering, validating, documenting and prioritizing vulnerabilities.
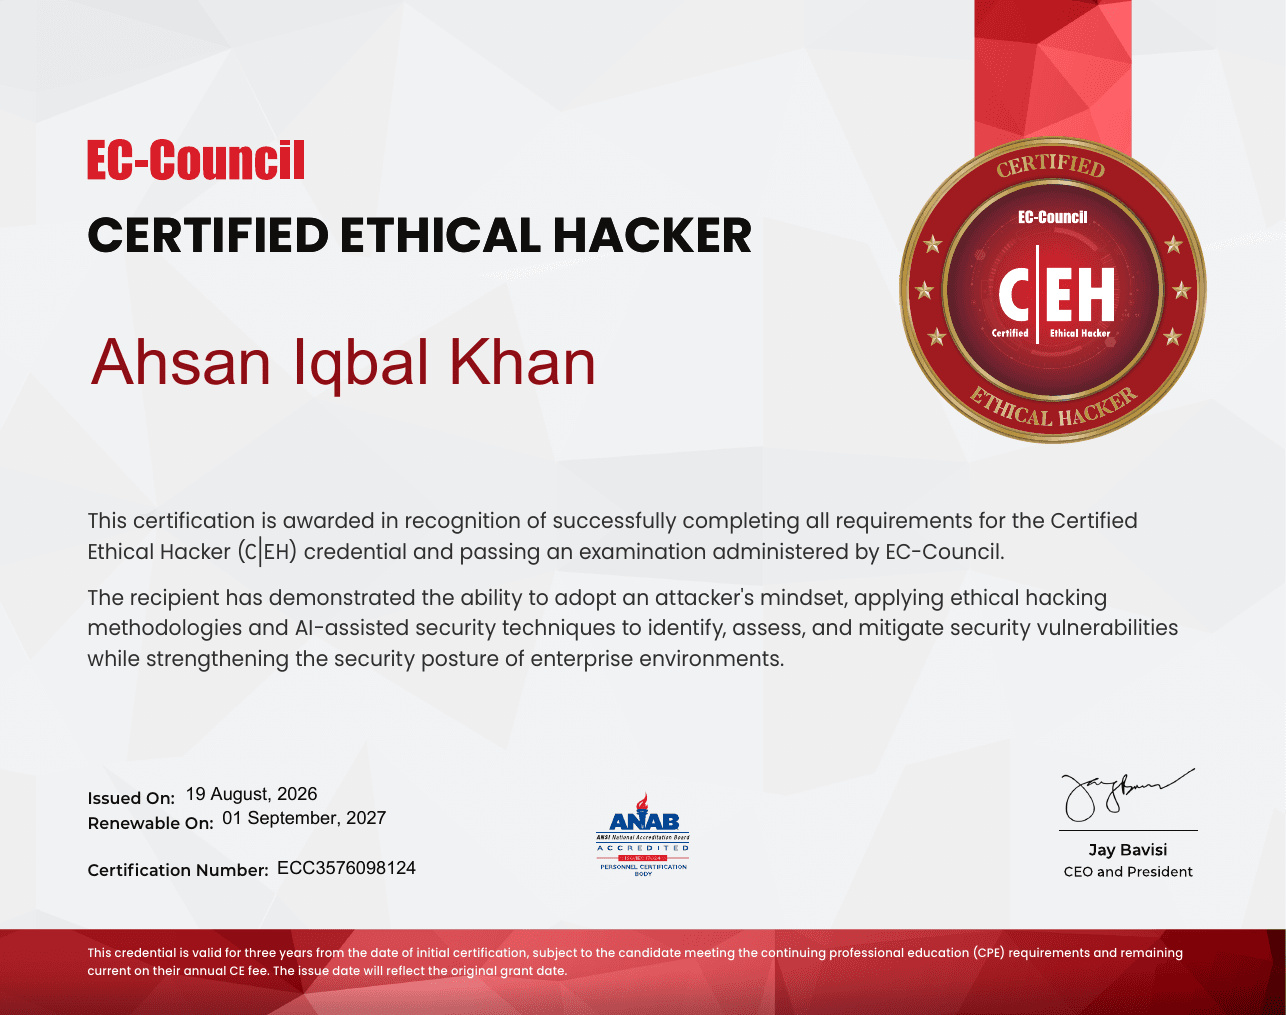
Ethical hacking methodologies, vulnerability assessment and security posture improvement.
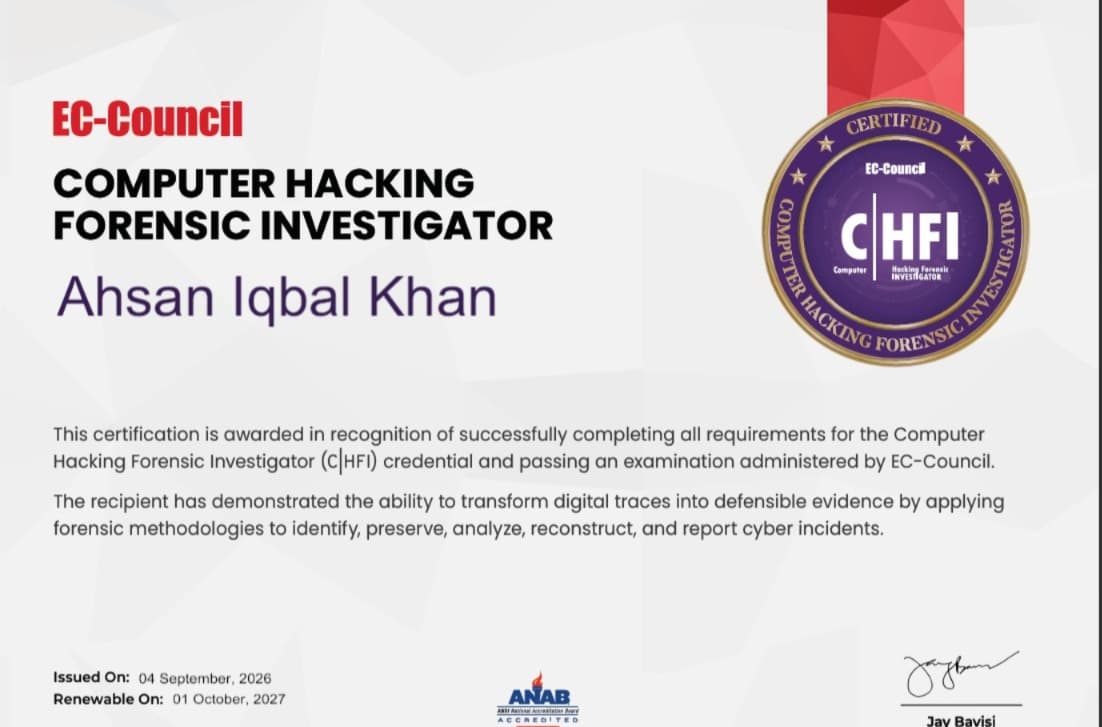
Digital evidence, forensic methodology, reconstruction and reporting of cyber incidents.
Structured review of security posture, common weaknesses and prioritized remediation guidance.
Alert triage, threat-oriented investigation thinking and security monitoring workflows.
OWASP-focused review of web application risks and security-aware delivery practices.
Planning, coordination, stakeholder communication, risk tracking and delivery oversight.
Clear technical findings, incident notes, remediation summaries and executive-ready communication.
Cross-functional coordination across technical, creative and security-adjacent workstreams.
If you need security-aware execution, structured project delivery, or someone who can bridge technical work with clear communication, let’s talk.